Understand your code
Read across repositories and components to understand how your system works.
AI security reviewer for engineering teams
Dokima reviews your repositories for security vulnerabilities and produces evidence and suggested fixes your developers can use.
Runs on Linux or macOS with your preferred AI model. Use Claude or Codex directly, or other models through OpenCode, including Gemini, open models and privately hosted local models.
Plans for teams of up to 5, 15 or 40 active contributors. Compare plans.
How it helps your team
Point Dokima at your local Git repositories. It keeps a record of the review and returns to work as your code changes.
Read across repositories and components to understand how your system works.
Check suspected issues and their evidence before adding them to the report.
See source locations, impact, verification reasoning and suggested fixes in an HTML report.
Review dashboard
The terminal dashboard keeps review stages, findings, evidence and validation status together.
Read the full sample report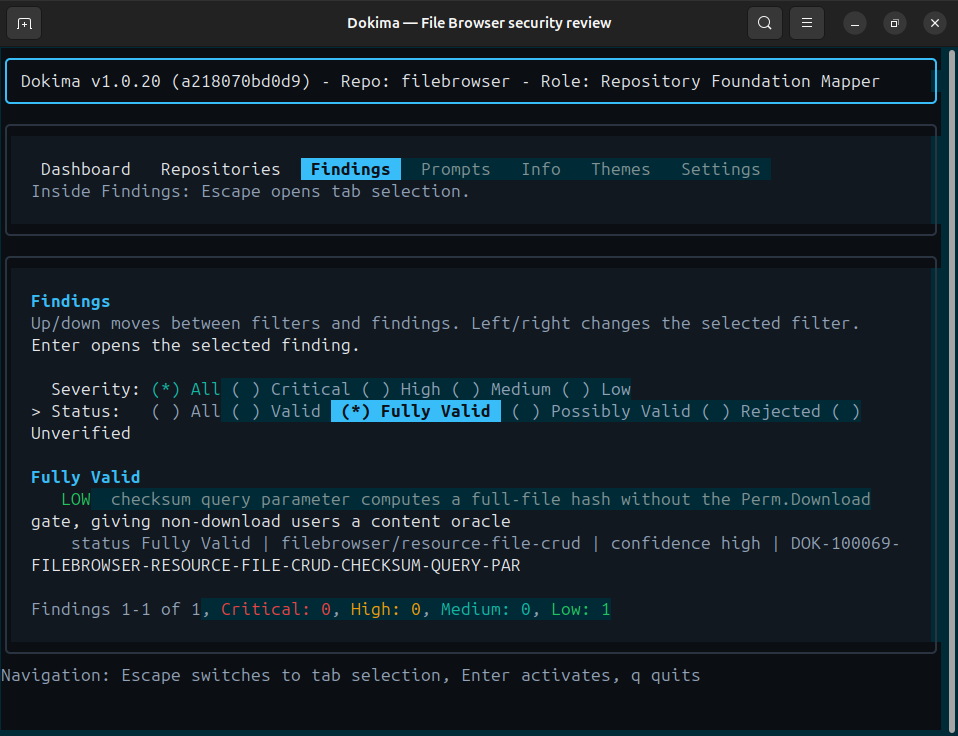
Before you begin
One or more Git repositories on Linux or macOS that your organisation is authorised to review.
Connect Claude or Codex directly, or use OpenCode for other providers and local models. Your model setup determines where code is processed.
Set up your runnerFollow the setup guide from installation to your first report. Review time and AI usage depend on your codebase and the work required.
Getting startedSee what Dokima finds
Start a full-product 21-day trial for your engineering team. No payment card required.